CNI / OT CYBERSECURITY
OT Network Segmentation and Industrial Security (UK)
Let data leave the control network without letting anything in
The short answer
Do you supply data diodes?
No. We do not supply data diodes or unidirectional gateways. What we do supply is the industrial networking layer around them: managed switches, serial gateways and routers configured for segmented OT networks, quoted per site. If you need a certified one-way boundary device, you need a specialist diode vendor.
Operators of substations, water treatment and rail need monitoring data out of the control network, but every outbound link is also a way in. Firewalls can be misconfigured, bypassed or turned around, and regulators no longer accept that as the only boundary. The exposure is a route from the corporate world, or the internet, straight into safety-critical OT.
Talk through your site ● Answered within one working day
The difference
OT network segmentation: what changes the day it goes live
Operators of substations, water treatment and rail need monitoring data out of the control network, but every outbound link is also a way in. Firewalls can be misconfigured, bypassed or turned around, and regulators no longer accept that as the only boundary. The exposure is a route from the corporate world, or the internet, straight into safety-critical OT.
- Hardware-enforced one-way data flow, so monitoring data leaves and nothing returns
- A boundary that cannot be reconfigured into a two-way path, unlike a firewall rule
- Segmented, managed switching built for substation and rail environments
- Evidence and architecture that map directly onto NIS and NCSC CAF expectations
What you get
- 01
Hardware-enforced one-way data flow, so monitoring data leaves and nothing returns
- 02
A boundary that cannot be reconfigured into a two-way path, unlike a firewall rule
- 03
Segmented, managed switching built for substation and rail environments
- 04
Evidence and architecture that map directly onto NIS and NCSC CAF expectations
What we supply at the IT/OT boundary
What this covers
Network segmentation, managed industrial switching, secure remote access and protocol gateways that terminate a field protocol before it reaches the corporate network.
What it does not
A hardware data diode. We do not currently stock a unidirectional gateway, and a managed switch with VLANs is not a substitute for one — a diode is a physical one-way path, an ACL is a configuration that can be changed.
If your design mandates a data diode, ask us and we will source it or tell you who can. We would rather lose the line than supply something that is not what the design calls for.
The full stack, applied here
One intrusion attempt, stopped at the OT boundary
Every Indiott build runs all five layers as one accountable system. Follow a single blocked intrusion from the sensor that catches it to the report that proves it.
The stack already meters what it protects: LoRaWAN sensors read cabinet temperature, door and environment so a physical tamper shows up with the network alarm.
Hands a physical alert to CONNECT ↓
Managed industrial switches and secure VPN routers form the OT backbone, so remote sites reach SCADA over encrypted 4G/5G rather than an exposed public path.
Hands a trusted link to SECURE ↓
The core: a hardware data diode enforces one-way flow to IEC 62443, VLAN and ACL segmentation isolates zones, and deep-packet firewalling blocks lateral movement.
Hands a clean stream to CONTROL ↓
Where the boundary must act, Serial-to-Modbus gateways and remote IO let a verified command through while raw serial never crosses the diode.
Hands an audited action to MANAGE ↓
OT-monitoring dashboards route intrusion, policy and asset alarms to the SOC and feed your SIEM over standard protocols, so every blocked event is logged and evidenced.
The loop is closed ✓
How teams start
From a single pilot to the whole portfolio
You do not boil the ocean. Nearly every rollout runs the same four moves, and you own a working, evidenced result at the end of the first one.
Scope & risk map
We walk the sites, list the assets and pin the one constraint that matters, then agree what a good result looks like before a single sensor is bought.
Pilot on one site
A focused set of sensors goes onto one site or asset group, live on our telemetry and dashboards, wired to the people who need the alert.
Validate & standardise
We tune thresholds, kill false positives, confirm the integration into your SCADA, BMS or CAFM, and write the standard design down so it repeats.
Scale the portfolio
The proven design rolls out across the estate, reusing the same hardware standards and data models so every site reads the same way.
The OT network segmentation kit we deploy
Full catalogue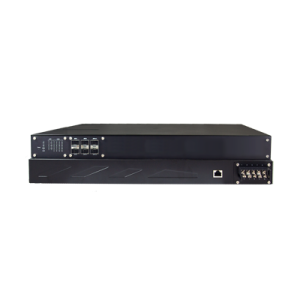 ATOP PG5900A Smart Grid Protocol Gateway (IEC 61850)
Request a price
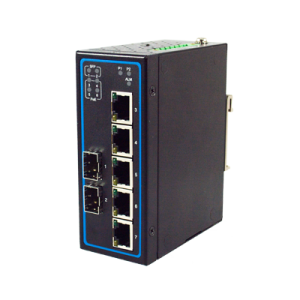 ATOP EHG7307 Industrial Managed Ethernet Switch
Request a price
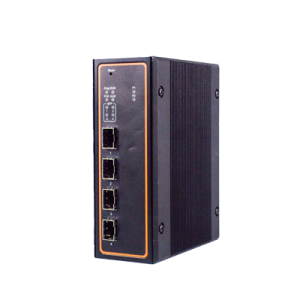 ATOP EHG7504 Industrial Managed Ethernet Switch
Request a price
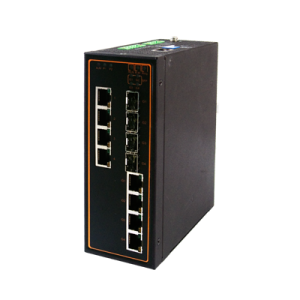 ATOP EHG7508 Industrial Managed Ethernet Switch
Request a price
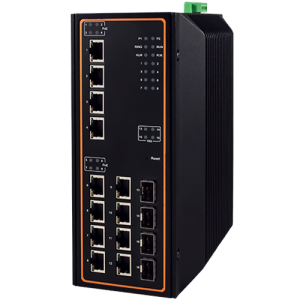 ATOP EHG7516 Industrial Managed Ethernet Switch
Request a price
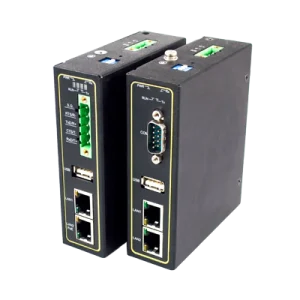 ATOP MB5901 Rugged Serial to Ethernet Modbus Gateway
Request a price
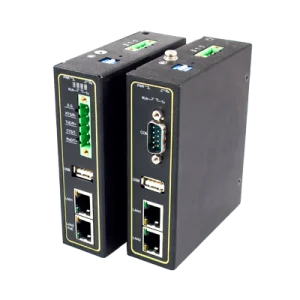 ATOP SE5901 Rugged Serial to Ethernet Device Server
Request a price
 ATOP SE5901 SDK Industrial Edge Computer
Request a price
| Model | Key specification | Price ex VAT | Availability |
|---|---|---|---|
| ATOP PG5900A Smart Grid Protocol Gateway (IEC 61850) PG5900A | Protocol Conversion: Ethernet to Ethernet only: Modbus TCP, DNP3 TCP/IP, IEC 60870-5-104, IEC 61850 | Price on request | Quote only |
| ATOP EHG7307 Industrial Managed Ethernet Switch EHG7307 | SFP fibre uplink ports: 2 x SFP (SFP1: 1000 Mbps / SFP2: 100/1000 Mbps), alongside 5 x 10/100/1000 RJ45 | Price on request | Quote only |
| ATOP EHG7504 Industrial Managed Ethernet Switch EHG7504 | PoE Power Budget: Up to 120 W across 4 IEEE 802.3af/at PoE ports (EHG7504-4PoE) | Price on request | Quote only |
| ATOP EHG7508 Industrial Managed Ethernet Switch EHG7508 | PoE Ports and Power Budget: 8 × 802.3af/at PoE ports, max 30 W per port, up to 240 W device budget | Price on request | Quote only |
| ATOP EHG7516 Industrial Managed Ethernet Switch EHG7516 | Port Configuration: 4 × 1G RJ45 + 8 × 1G SFP + 4 × 1/10G uplink SFP, no PoE ports | Price on request | Quote only |
| ATOP MB5901 Rugged Serial to Ethernet Modbus Gateway MB5901 | Ethernet connector ports: RJ45 x 2 (dual-port, with 802.1D-2004 RSTP redundancy) | Price on request | Quote only |
| ATOP SE5901 Rugged Serial to Ethernet Device Server SE5901 | Ethernet Ports and Redundancy: 2 × 10/100BASE-T(X) RJ45 with RSTP, -40°C to +85°C | Price on request | Quote only |
| ATOP SE5901 SDK Industrial Edge Computer SE5901-SDK | CPU and Memory: ARM 800 MHz, up to 256 MB RAM, up to 128 MB flash | Price on request | Quote only |
Brands in this kit: Atop Technologies
Why Indiott
A specialist stack, not a box-shifter
Brand-agnostic by design
We pick the best of each brand for the layer and the environment, not one vendor catalogue. Milesight, AquaIoT, Atop, Browan, SpecSens and Urban.io, chosen on merit.
The whole stack, one supplier
Sensing, connectivity, OT security, control and the dashboard come from one accountable team, so there is no finger-pointing when something needs to talk to something else.
Specified and supported in Britain
UK-based engineers scope the site, quote the kit and stand behind it, with compliance mapped to the regimes your auditors actually cite.
Honest kit, honest pricing
Prices are shown where we can, quoted fast where we cannot, and you get a straight answer and a bill of materials within one working day.
 DEPLOYED IN THE FIELD
Compliance this answers to
| Standard | What it requires |
|---|---|
| IEC 62443 | the OT security standard our switching and diode hardware is built to |
| NIS Regulations and NCSC CAF | unidirectional boundaries are a recognised control for essential services |
| EN 50155 rail and IEC 61850-3 substation | environmental and EMC ratings for the deployment context |
What it costs, roughly
A data diode boundary is a considered capital purchase, not an impulse buy, and several of these lines are quote-only by manufacturer policy. The right comparison is against the cost and regulatory exposure of an OT incident, which runs to far more. Tell us the boundary you need to protect and we return options and indicative pricing within one working day.
Frequently asked questions
How do you segment an OT network in practice?
You split the plant into zones by function and risk, following the Purdue model, and allow traffic between them only through defined conduits. Managed switches enforce VLANs and port isolation, while an industrial router like the UR35 (from £149.63) firewalls the boundary between OT, IT and any remote link.
How is secure remote access provided to a site?
Through an encrypted, authenticated tunnel rather than an open port. The UR35 industrial cellular router (from £149.63 ex VAT) and 5G UR75 (from £460.12) terminate IPsec or OpenVPN, so an engineer reaches a specific device over a VPN with the firewall denying everything else. This removes exposed remote-desktop or direct-to-PLC access, a common route into OT.
Which standards and regulations apply to CNI in the UK?
IEC 62443 is the core standard for industrial automation and control system security, covering zones, conduits and security levels. UK operators of essential services also fall under the NIS Regulations 2018, assessed against the NCSC Cyber Assessment Framework. The architecture here, segmentation plus controlled access plus monitoring, maps directly onto those requirements.
Can I secure legacy serial PLCs and RTUs?
Yes. Legacy Modbus RTU and serial devices are brought onto a controlled network through secure serial-to-Ethernet gateways, then isolated behind the router firewall and VLANs. This lets you wrap modern segmentation and access control around equipment that has no built-in security, without replacing the PLC or RTU itself.
Does adding security break real-time control?
It should not. Segmentation and firewalling operate at the network boundary, and industrial routers and switches are built for deterministic OT traffic and wide temperature ranges. Rules are written to permit the specific protocol flows control needs, such as Modbus TCP or DNP3, and deny the rest, so latency-sensitive control stays inside its zone.
Where do you start on an existing plant?
Start by mapping assets and traffic to see what actually communicates, then define zones and the conduits between them. Add a firewalled router at the OT boundary, replace flat switching with VLAN-capable managed switches, and route all remote access through the VPN. This is an incremental hardening path rather than a rip-and-replace.
Do you supply a hardware data diode?
Not currently. We supply network segmentation, managed industrial switching, secure remote access and protocol gateways that terminate a field protocol before it reaches the corporate network. A managed switch with VLANs is not a substitute for a diode — a diode is a physical one-way path, an ACL is a configuration that can be changed. If your design mandates a data diode, ask and we will source it or tell you who can.
Buying this in the UK
- Industrial networking hardware for segmented OT networks, quoted per site. We do not supply data diodes.
- Supplied by Indiott, a trading name of PSI Technologies Limited (Companies House 03689664, VAT GB 730 2340 83), Hampshire, United Kingdom.
- Every price is published ex VAT at indiott.com — no quote needed to see it.
- Typically dispatched within 14 working days from the UK, on a VAT invoice.
- Call 023 9223 3611 or request a quote.
Next step
Scope it with an engineer.
Tell us the site, the assets and the constraint. You get a bill of materials and a straight answer within one working day.
- A bill of materials sized to your site
- Priced ex VAT, UK entity, no login wall
Rather talk it through? Call 023 9223 3611
Received. An engineer has it.
You will hear back within one working day with the parts, the prices and the lead time. A confirmation is on its way to your inbox.
If it is urgent, call 023 9223 3611.